A developer ships version 1.4.0, then reinstalls Android Studio on a new laptop. The old keystore was in a folder they never backed up. The next release is rejected, and every tutorial they find says the app is finished — which is not true, but nothing on screen explains why.
Two different keys are involved. One you hold, and losing it is recoverable. The other signs what users install, and Google holds it when Google Play App Signing is enabled. Most signing panic comes from treating those as one key, or from registering the wrong certificate fingerprint with Firebase and assuming the reset broke the integration.
This guide separates the two keys, explains keystores and fingerprints, walks through a documented upload-key reset, and covers what changes for API integrations and older Android versions.
What Is Google Play App Signing?
Android requires every APK to be digitally signed before it can be installed or updated. The signature is how the platform knows that an update genuinely comes from the same publisher as the installed app — without it, any app could overwrite another by using the same package name.
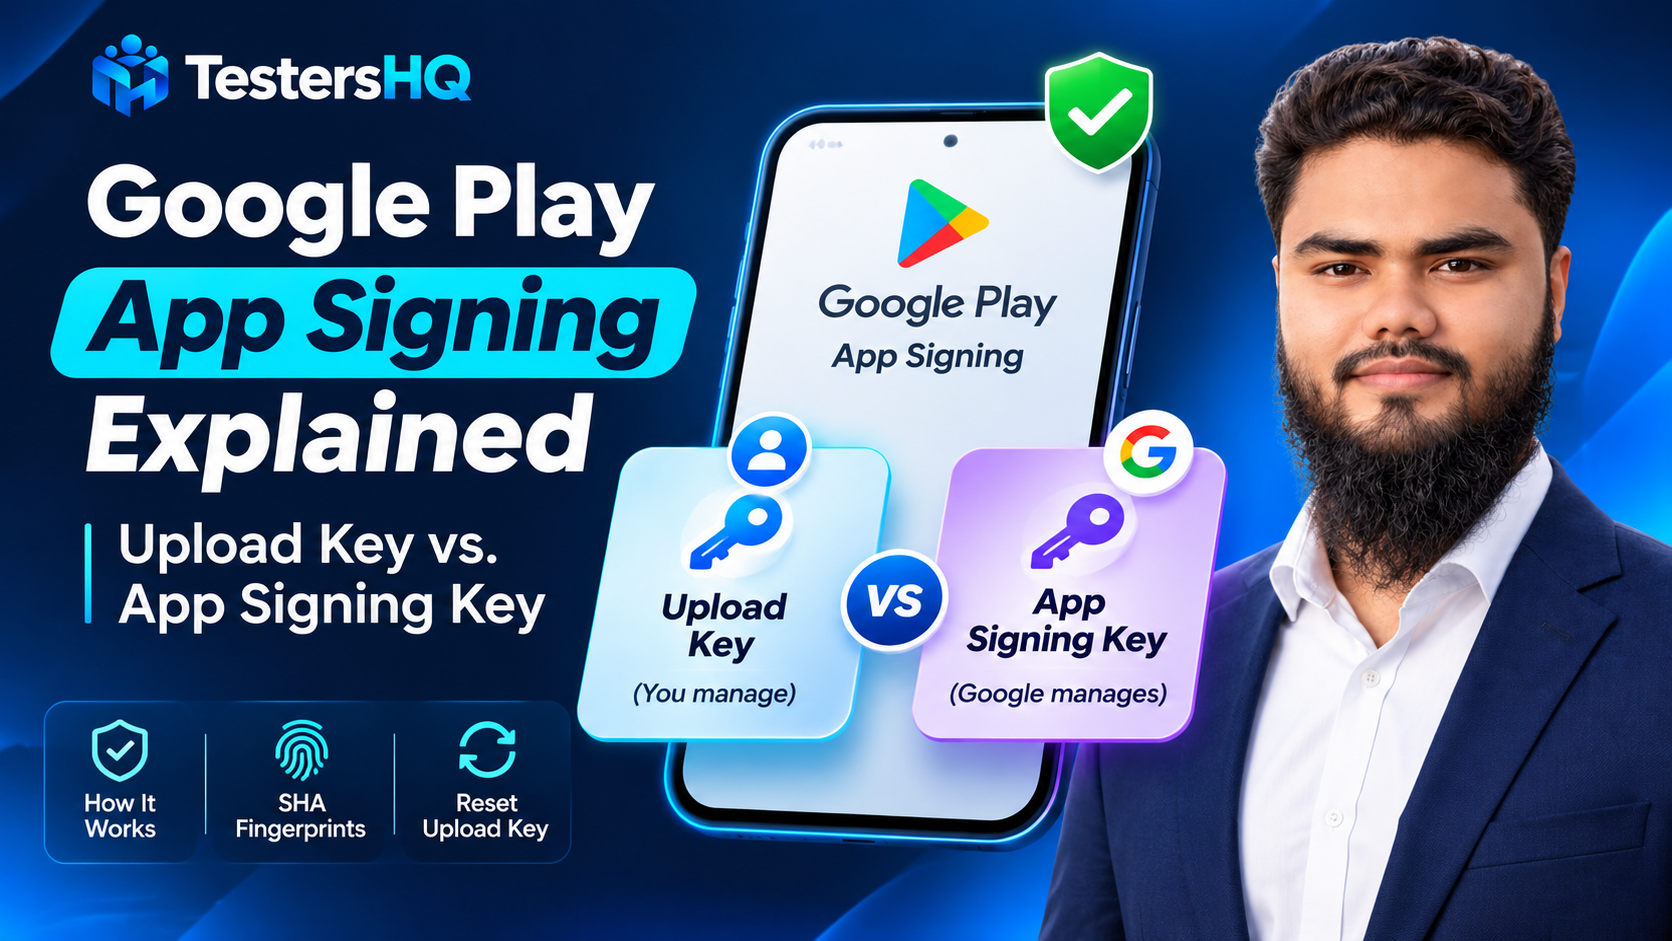
Google Play App Signing changes who performs the final signing step. Instead of you signing the APK that users download, you sign the Android App Bundle with an upload key you control, and Google signs the APKs it generates from that bundle with an app signing key it manages.
Google describes the benefit plainly: it protects the signing key on the same infrastructure it uses for its own keys, backed by Google's Key Management Service. It also unlocks app bundle behaviour such as optimised delivery, because the bundle defers APK building and signing to Play.
Two facts set the boundary. Play App Signing is required when you publish an app to Google Play for the first time, and it is optional for apps created before August 2021 that continue distributing self-signed APKs. Setting it up requires admin permission on the account.
How Google Play App Signing Works
- You create an upload key and keystore, in Android Studio or with
keytool. - You sign the app bundle with that upload key.
- You upload the signed
.aabto Play Console. - Google verifies the bundle against your registered upload certificate.
- Google generates the distribution APKs and signs them with the app signing key.
- Devices download and install APKs signed by that app signing key.
One detail worth knowing: when Google signs the APKs it also adds two manifest stamps, com.android.stamp.source and com.android.stamp.type, so a delivered APK remains traceable to the original uploader.
Upload Key vs. App Signing Key — What's the Difference?
The table below is the reference to keep. The two rows that cause the most confusion are the last two: which key touches the bundle, and which touches what users install.
| Feature | Upload key | App signing key |
|---|---|---|
| Who controls it | You, and you must keep it secret | Google Play, unless you supplied your own key |
| Main purpose | Proves your identity to Google Play at upload | Signs the APKs installed on user devices |
| Where it lives | A Java keystore (.jks or .keystore) on your machine or CI | Google's key management infrastructure |
| Associated certificate | Upload certificate, exportable as .der or .pem | App signing certificate, downloadable as a public .der |
| Key size | RSA 2048-bit or larger | RSA 4096-bit for Google-generated keys; 2048-bit or larger for custom keys |
| If lost | Recoverable: request an upload key reset | Not your problem if Google generated it; unrecoverable if you self-managed it |
| Can it be changed | Yes, through a reset; you can also rotate it freely | Yes, through a key upgrade with version-dependent enforcement |
| Signs the uploaded AAB | Yes | No |
| Signs APKs from Play | No | Yes |
Developer tip: Google recommends keeping the upload key and app signing key different. Enrolling with a Google-generated app signing key and a separate upload key gives you the reset safety net and keeps the two roles cleanly divided.
What Is an Android Keystore?
A keystore is not a key. It is a binary repository that stores one or more private keys together with their certificates. Android Studio produces .jks files by default; the older .keystore extension is the same idea.
- Alias — the name of an entry inside the keystore. One keystore can hold several keys, so build tools need the alias to know which to use.
- Private key — the secret material that produces signatures. It never leaves the keystore.
- Certificate — the public half plus identifying metadata: owner and expiry.
- Keystore password unlocks the container; the key password protects the individual entry. Android Studio sets them to match by default.
Google recommends a validity of at least 25 years so the same key can sign updates for the life of the app. To inspect what a keystore actually contains, use keytool. This prints the certificate details, including the SHA-1 and SHA-256 fingerprints:
keytool -list -v -keystore upload-keystore.jks -alias uploadkeytool prompts for the password interactively, so it never needs to appear in a command line or a shell history file. Filenames and aliases above are examples; use your own.
Security warning
- Never share a keystore file, a private key, or a keystore password with anyone — including in a support thread, a chat group, or an AI assistant.
- Never commit a keystore or its passwords to a public repository. Store secrets in your CI secret store, not in
build.gradle. - Share only the public certificate when a service asks for one. It contains no private key.
How to Find SHA-1 and SHA-256 Fingerprints in Play Console
Both the upload certificate and the app signing certificate are published on the Play app signing page, and the MD5, SHA-1 and SHA-256 fingerprints appear alongside them. The path per current Google documentation:
- Sign in to Play Console and select your app.
- Open Protected with Play.
- Go to Play Store protection.
- Select Manage Play app signing.
- Scroll to the App signing key section to see the app signing certificate and its fingerprints.
- Check the Upload key certificate section for the upload certificate.
Interface labels change. Older Android documentation still refers to a Release → Setup → App signing path, and your console may group these pages differently. If you cannot find the page, search the console for "app signing" rather than trusting a screenshot from an older guide — including this one.
You can also download the original .der certificate from the same page and compute fingerprints locally, which is useful when a provider wants a hash format the console does not display.
Which SHA Fingerprint Should You Use?
Three different certificates can exist for one app, and each corresponds to a different build. A fingerprint is only useful to a provider if it belongs to the build that provider will actually see.
| Situation | Which certificate | Why |
|---|---|---|
| Firebase, Google Sign-In, Maps, OAuth in a store build | App signing certificate | Users run APKs signed by Google, not by your upload key |
| A release build installed directly on a device | Upload certificate | That build carries your upload signature, not Play's |
| Local debugging and emulator runs | Debug certificate | The SDK tools sign debug builds automatically with it |
Android App Links (assetlinks.json) | App signing certificate, plus others you need to verify | Verification must accept the builds users actually install |
| An app using quantum-ready hybrid signing | All three signing keys | Google documents three distinct keys for this configuration |
Exact provider requirements vary, so read the integration's own documentation rather than assuming. A practical rule covers most cases: register the app signing certificate for anything that authenticates the version users install from Google Play, and add the debug or upload certificate only when a provider must also accept a locally built build. If the integration depends on App Links or runtime permissions, the Android app permissions guide covers the surrounding setup.
Quantum-ready signing needs extra attention. Current Google documentation describes a hybrid configuration combining a classical RSA 4096-bit key with a post-quantum ML-DSA-65 key. Google generates a separate classical key for devices below Android 17, so the app uses three distinct keys. Android 17 and higher verify via APK signature scheme v3.2; older devices keep verifying against the classical signature blocks. For that configuration, the documented guidance is to register all three keys' fingerprints with your API providers. New apps are enrolled this way with Google-generated keys by default.
What Happens If You Lose Your Upload Key?
If Play App Signing is enabled and the app signing key was generated by Google, losing the upload key does not lock you out. You cannot sign new uploads until the key is replaced, but Google can reset it, and the app stays live in the meantime.
The contrast case is what causes real damage. For an app with no Play App Signing, or where you supplied your own app signing key and then lost it, Google's documentation is direct: if you lose your app's signing key, you lose the ability to update your app. That is a property of Android's secure update model — a different key cannot update an installed app.
Two clarifications that prevent unnecessary panic:
- A reset replaces the upload key only. The app signing key is untouched, so existing installs keep updating, and fingerprint registrations stay valid.
- Losing the keystore is not losing the store listing. Installs, reviews and ranking history are unaffected by an upload key problem.
The one thing you cannot do until the reset is effective is publish a new release. Plan for that gap if you are close to a deadline.
How to Reset a Lost Upload Key
The documented sequence, with the current console path:
- Generate a new upload key in Android Studio (Build → Generate Signed Bundle/APK → Create new).
- Export the public certificate to PEM format with
keytool, using the command below. - Open the Play app signing page: Protected with Play → Play Store protection → Manage Play app signing.
- In the "Upload key certificate" section, select Request upload key reset.
- Enter the reason and upload the
.pemfile, then select Request. - Follow the status shown in Play Console. Wait until the reset has taken effect before relying on it.
- Sign every future upload with the new key. Keep the old keystore archived in case you need to verify an old build's signature.
keytool -export -rfc -keystore upload-keystore.jks -alias upload -file upload_certificate.pemThat command is Google's documented example. The filename, alias, and output path are placeholders — substitute your own values, or you will export the wrong certificate and the request will not match the key you intend to use.
A reset does not repair API authentication by itself. If Firebase or Google Sign-In was failing because someone registered the upload certificate instead of the app signing certificate, replacing the upload key changes nothing about that mismatch — fix the registration instead.
Can You Change or Upgrade Your App Signing Key?
Yes, through a documented key upgrade, and the reasons are narrow: the existing key was compromised, or you need a cryptographically stronger one. Google documents an annual key upgrade for all installs on Android 17 (API level 37) or higher.
From the Play app signing page, open the App signing key section and select Upgrade key. You then choose whether Google generates a new key (the recommended path), reuses another app's key in the same account, or accepts a copy of a key you supply. Register the new fingerprints with your API providers afterwards.
Enforcement differs by Android version, which is the part that catches people out:
- Android 17 (API 37) and higher strictly enforces the upgraded quantum-ready hybrid key, verified through APK signature scheme v3.2.
- Android 13 to 16 (API 33–36) strictly enforces your latest classical key, through APK signature scheme v3.1.
- Android 7 to 12 (API 24–32) does not enforce the upgraded key and still recognises the legacy classical key. Google Play Protect adds validation that updates carry your latest classical key, unless the user has turned that off.
That last point has a concrete consequence: if you share one key across several apps to share data, devices on Android 12 or lower will only recognise the legacy key for features such as custom permission sharing. Older installations continuing on a legacy certificate is expected behaviour, not a bug.
Common App Signing Errors and How to Troubleshoot Them
Treat this as a diagnosis table, not a list of exact console strings — Google does not commit to fixed error copy, and messages change.
| Problem | Possible cause | Recommended action |
|---|---|---|
| Upload rejected for a certificate mismatch | Signed with a key other than the registered upload key | Compare signatures with jarsigner -verify -verbose -certs your.aab on both builds |
| Wrong keystore or alias selected | Multiple keystores on the machine, or a stale signing config in Gradle | List entries with keytool -list -keystore, then fix the alias in CI and local config |
| Password fails on a keystore that used to work | A different key/keystore password pair, or a corrupted or truncated copy | Restore the backup before retrying; check that the file size matches the original |
| Update rejected because the app was signed with the wrong key | A rebuilt machine or a new team member generated a fresh key | Sign with the registered upload key; if it is genuinely gone, request a reset |
| Firebase or Google Sign-In fails in the Play build only | Only the upload or debug fingerprint was registered | Add the app signing certificate's SHA-1 and SHA-256 from the Play app signing page |
| App Links stop verifying | assetlinks.json lists an outdated fingerprint | Update the file with the current app signing fingerprints and republish it |
| Locked out of uploads after losing a keystore | Upload key lost while Play App Signing is enabled | Request an upload key reset with a new PEM certificate |
The signature comparison from Google's update documentation is the fastest way to settle a mismatch: run the command on the previous and the new bundle and compare the output. If they match, you are using the same key. When a mismatch turns out to be a genuine defect rather than a key problem, the bug report guide covers reporting it so someone else can reproduce it.
App Signing Security Best Practices
- Keep at least two offline backups of the upload keystore, in separate locations, and test that you can restore one.
- Store private keys encrypted at rest and never in a public repository, even briefly.
- Use strong passwords unique to signing, held in a password manager rather than in a file beside the keystore.
- Restrict release credentials to the people who publish, and to CI secrets with the narrowest scope that works.
- Enforce 2-Step Verification for every user with Play Console access — Google documents this as baseline protection.
- Keep a record of public certificate fingerprints per app, so a mismatch is obvious without opening the console.
- Document the release signing process: who holds the keystore, where backups live, and what to do if it is lost.
- Use a separate upload key per app where practical, so one compromised key has the smallest blast radius.
Google Play App Signing Checklist
Run through this before the first release, and again whenever signing configuration changes.
- Upload key generated with RSA 2048-bit or larger, with at least 25 years validity.
- Upload key distinct from the app signing key.
- Keystore backed up in two separate locations, both tested.
- Alias, keystore password, and key password recorded in a password manager.
- Play App Signing configured on the Play app signing page.
- App signing certificate fingerprints copied from Play Console, not from a local keystore.
- Those fingerprints registered with Firebase, Google Cloud, and any other API provider you use.
assetlinks.jsonupdated if the app uses App Links.- Existing releases verified to share the previous signature, using
jarsigner -verify. - 2-Step Verification enforced for all Play Console users.
- Release build tested through internal app sharing so you test what Play actually delivers.
Frequently Asked Questions
Is Google Play App Signing mandatory for new apps?
It is required when you publish to Google Play for the first time. Apps created before August 2021 may continue distributing self-signed APKs.
What is the difference between an upload key and an app signing key?
The upload key signs the bundle you send to Play and proves your identity. The app signing key signs the APKs Google delivers to users. You hold the first; Google holds the second unless you supplied your own.
Can I reset my upload key?
Yes. Generate a new key, export the public certificate to PEM, then request a reset from the Upload key certificate section of the Play app signing page.
Will resetting my upload key affect existing users?
No. The app signing key is unchanged, so installed apps keep updating normally.
Can I download my private app signing key from Google Play?
No. Google states you cannot retrieve a copy once Play App Signing is configured, and may retain a backup for disaster recovery. You can download a signed universal APK for distribution elsewhere.
Which SHA-1 fingerprint should I add to Firebase?
The app signing certificate's fingerprint, because that signs the build users install. Add the debug or upload certificate only if locally built builds must also authenticate.
Do I need both SHA-1 and SHA-256?
Depends on the integration. Play Console shows MD5, SHA-1 and SHA-256 for both certificates; register what the provider asks for.
What happens if I lose my keystore?
With Play App Signing and a Google-generated app signing key, request an upload key reset and continue. Without Play App Signing, losing the signing key means you can no longer update the app.
Can I use the same signing key for multiple app stores?
Yes. Either have Google generate the key and download a signed universal APK for the other stores, or generate the key yourself and provide a copy when configuring Play App Signing.
Does changing an app signing key affect older Android devices?
It can. Android 17+ enforces the upgraded hybrid key, Android 13–16 enforces your latest classical key, and Android 7–12 does not enforce the upgrade and still recognises the legacy key, with Play Protect adding validation.
Official Resources
- Use Play App Signing — key concepts, quantum-ready signing, API provider registration, key upgrades and resets
- Sign your app — keystores, certificates, signing for release, and Play App Signing setup
- Update or unpublish your app — the signature, package name and version code requirements for updates
- How app updates work — signing lineage and cross-store update behaviour
- APK signature schemes — the platform-side verification that makes all of this enforceable
Conclusion
Almost every signing problem reduces to one question: which key are we talking about? The upload key is yours, it signs bundles, and it can be replaced. The app signing key signs what users install, and when Google generates it, it is one thing you no longer have to fear losing.
The second recurring problem is a fingerprint registered against the wrong build. Copy the app signing certificate's fingerprint from Play Console for anything that authenticates the Play-distributed app, and add debug or upload fingerprints only where a local build must also work.
Back up the keystore in two places, keep the passwords somewhere you will still have in a year, and enforce 2-Step Verification on the account that can reset all of it. For what to verify before an update goes out, the closed testing checklist covers the release steps and the real device testing guide covers install verification on hardware you do not own. After release, the Android Vitals guide covers watching what happens. TestersHQ works with developers on that pre-release validation step.